SentryInsight case study
Exploitation Intelligence Reports
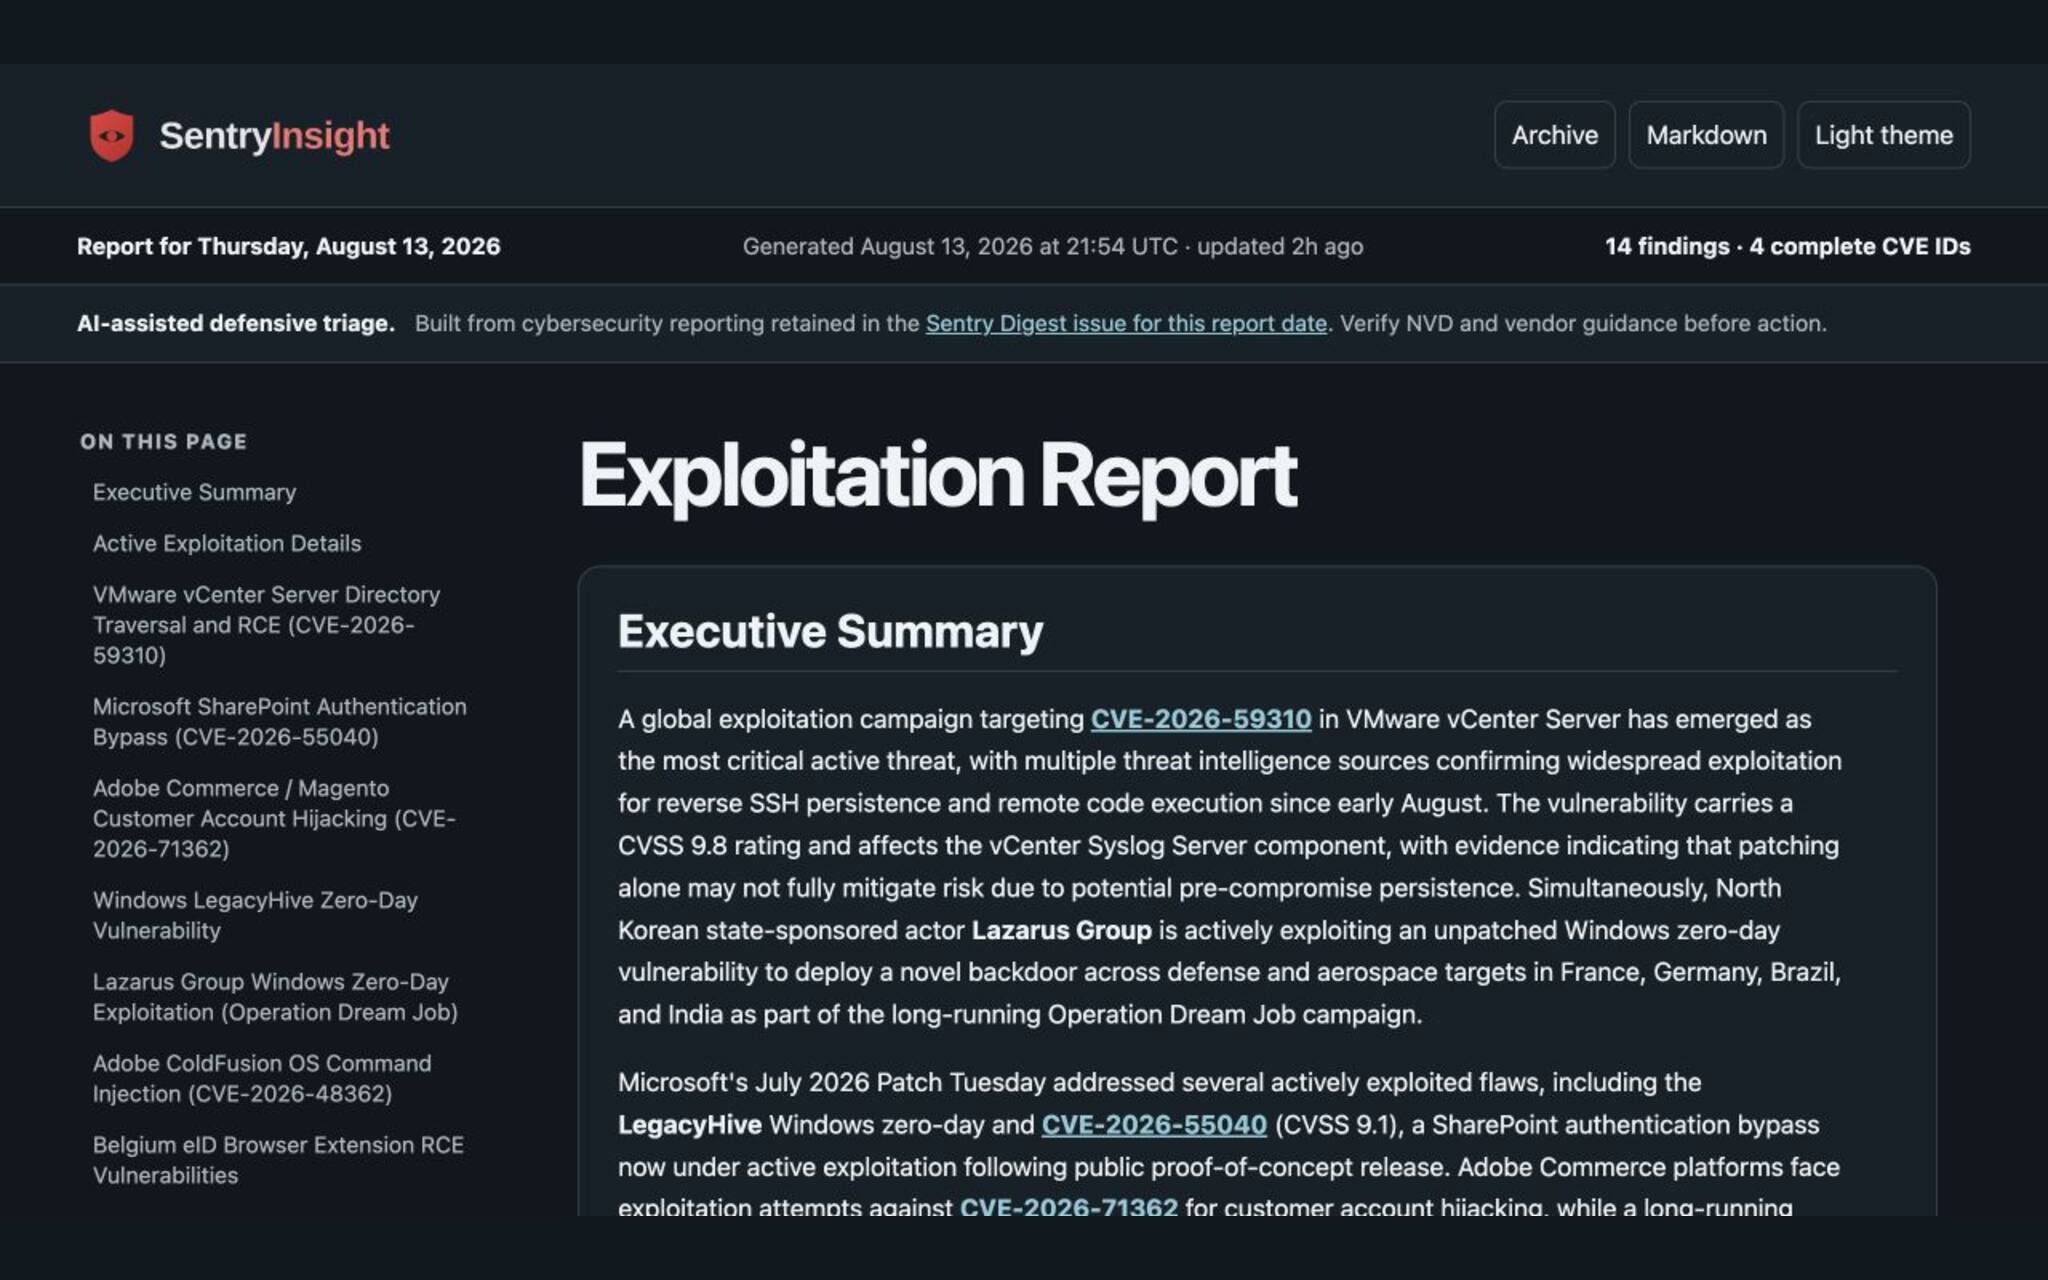
SentryInsight turns CVE and exploitation evidence into dated reports that connect affected systems, attack context, and response priorities. If a new run is not trustworthy, it preserves the last verified report.
- Python
- LangGraph
- Pydantic
- OpenRouter
What this project changes
- Built for
- Threat analysts and incident responders evaluating active exploitation risk.
- The problem
- CVE notices often separate vulnerability details from affected systems, exploitation evidence, and the response context needed to prioritize work.
- The outcome
- SentryInsight publishes dated exploitation reports that connect CVE evidence, affected systems, attack context, and response priorities.
- Why it can be trusted
- Fail-closed publishing prevents an untrustworthy run from replacing the last verified report, while dated archives preserve what changed.