SentrySearch case study
Threat Intelligence Research Workspace
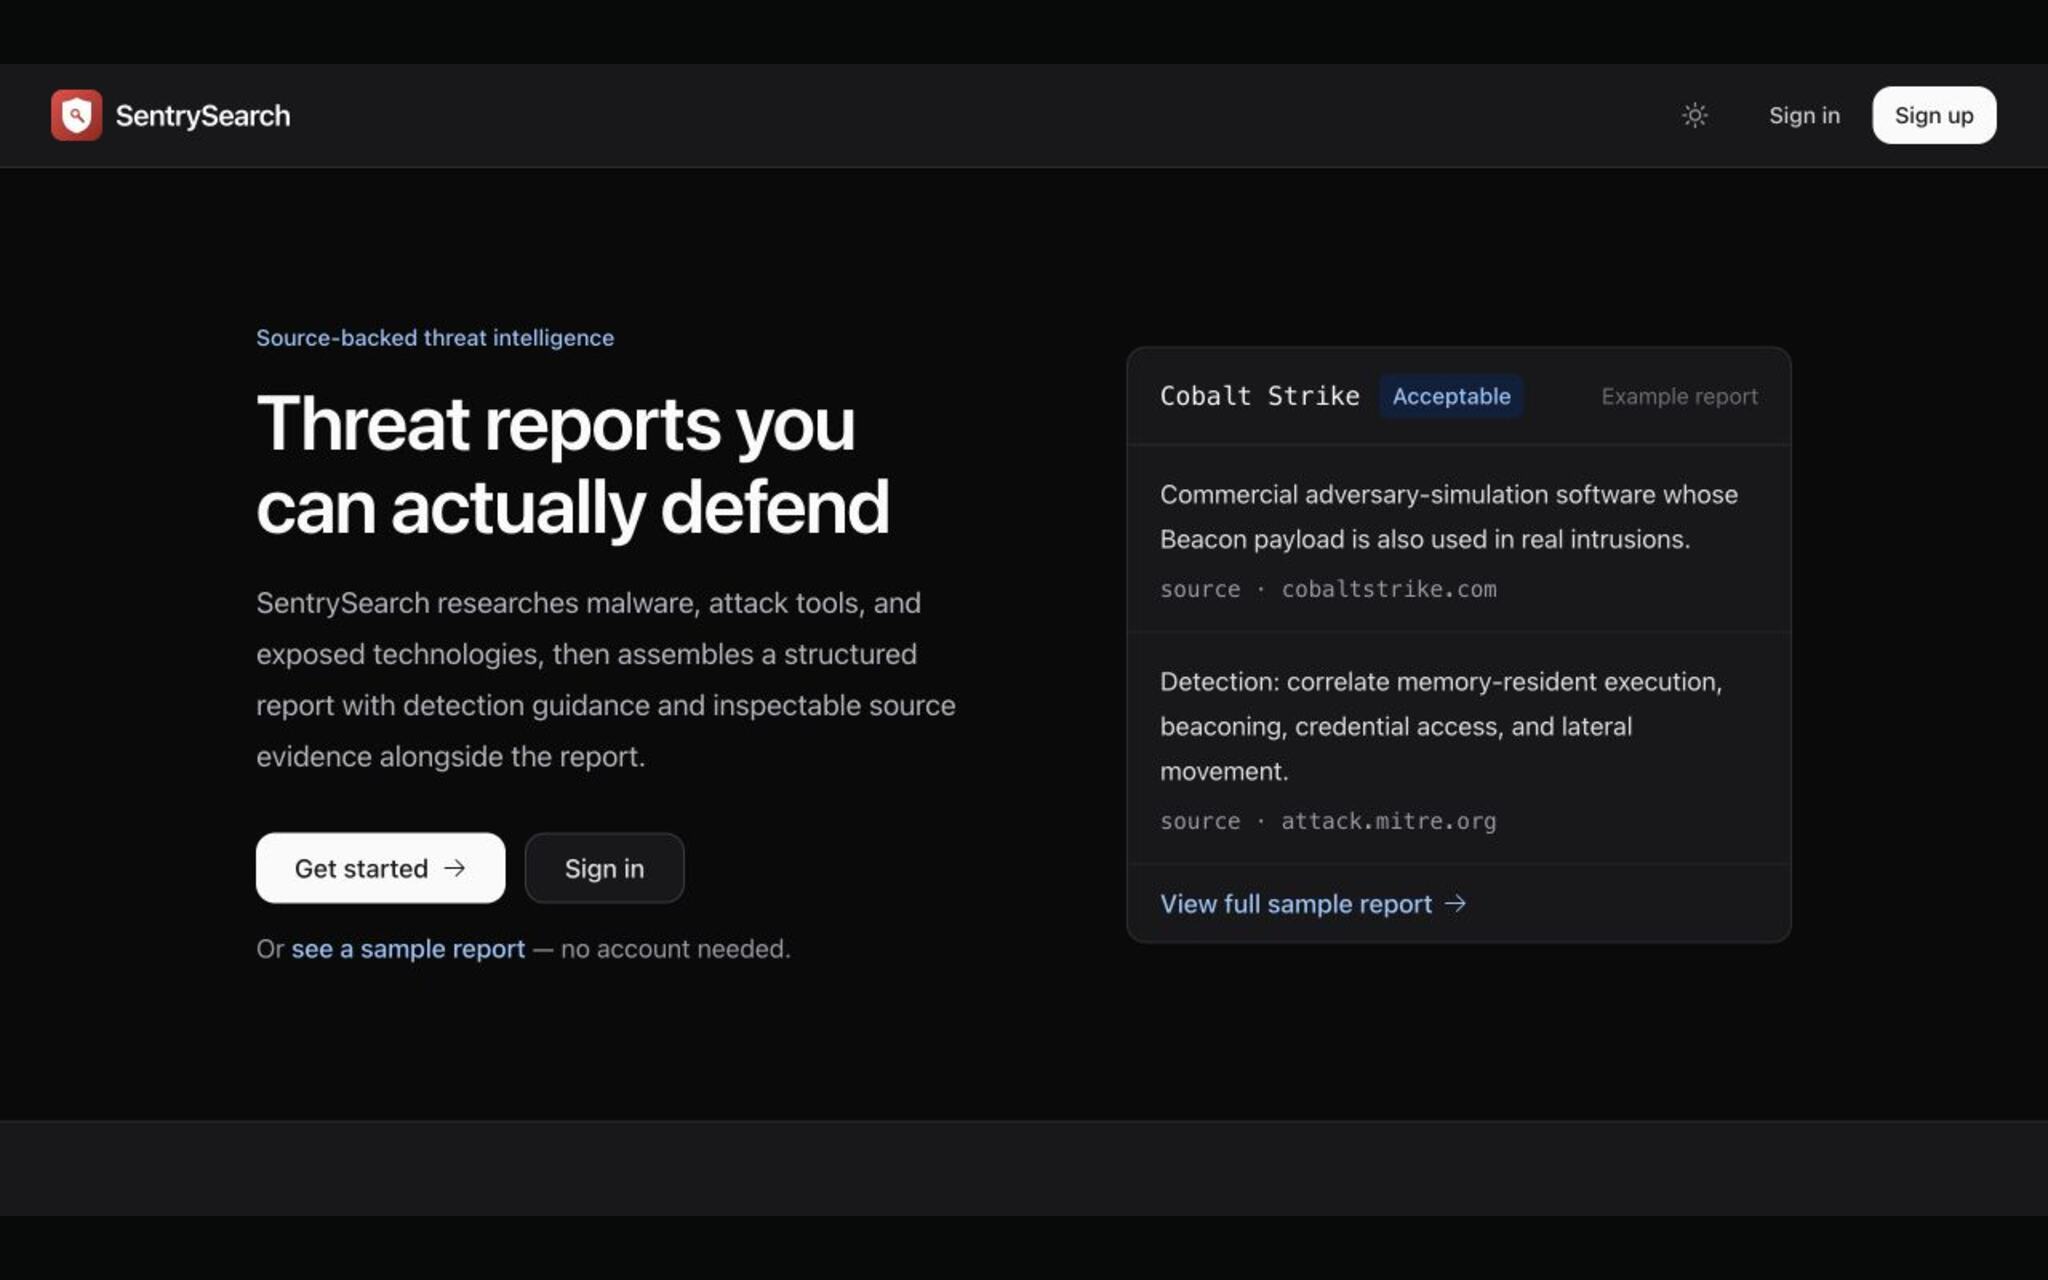
For threat analysts who need research they can defend, SentrySearch turns malware, attack tools, and exposed technologies into source-backed reports with detection guidance, a persistent report library, and explicit evaluation status.
- Next.js
- TypeScript
- FastAPI
- PostgreSQL
- Supabase
- AWS S3
What this project changes
- Built for
- Threat analysts and detection engineers who need research they can defend and reuse.
- The problem
- Research about malware, attack tools, and exposed technologies is scattered across sources, easy to lose, and difficult to translate into detection work.
- The outcome
- SentrySearch assembles source-backed profiles with persistent reports, authenticated library search, and detection guidance in one reviewable workspace.
- Why it can be trusted
- The report keeps source evidence attached and exposes evaluation status when a section could not be scored instead of presenting an unsupported result.